Built for teams shipping more than one app.
Paste two lines into each app and ship. A $crisp-compatible SDK so migrating is
copy-paste. HMAC identity verification so you always know which customer you're
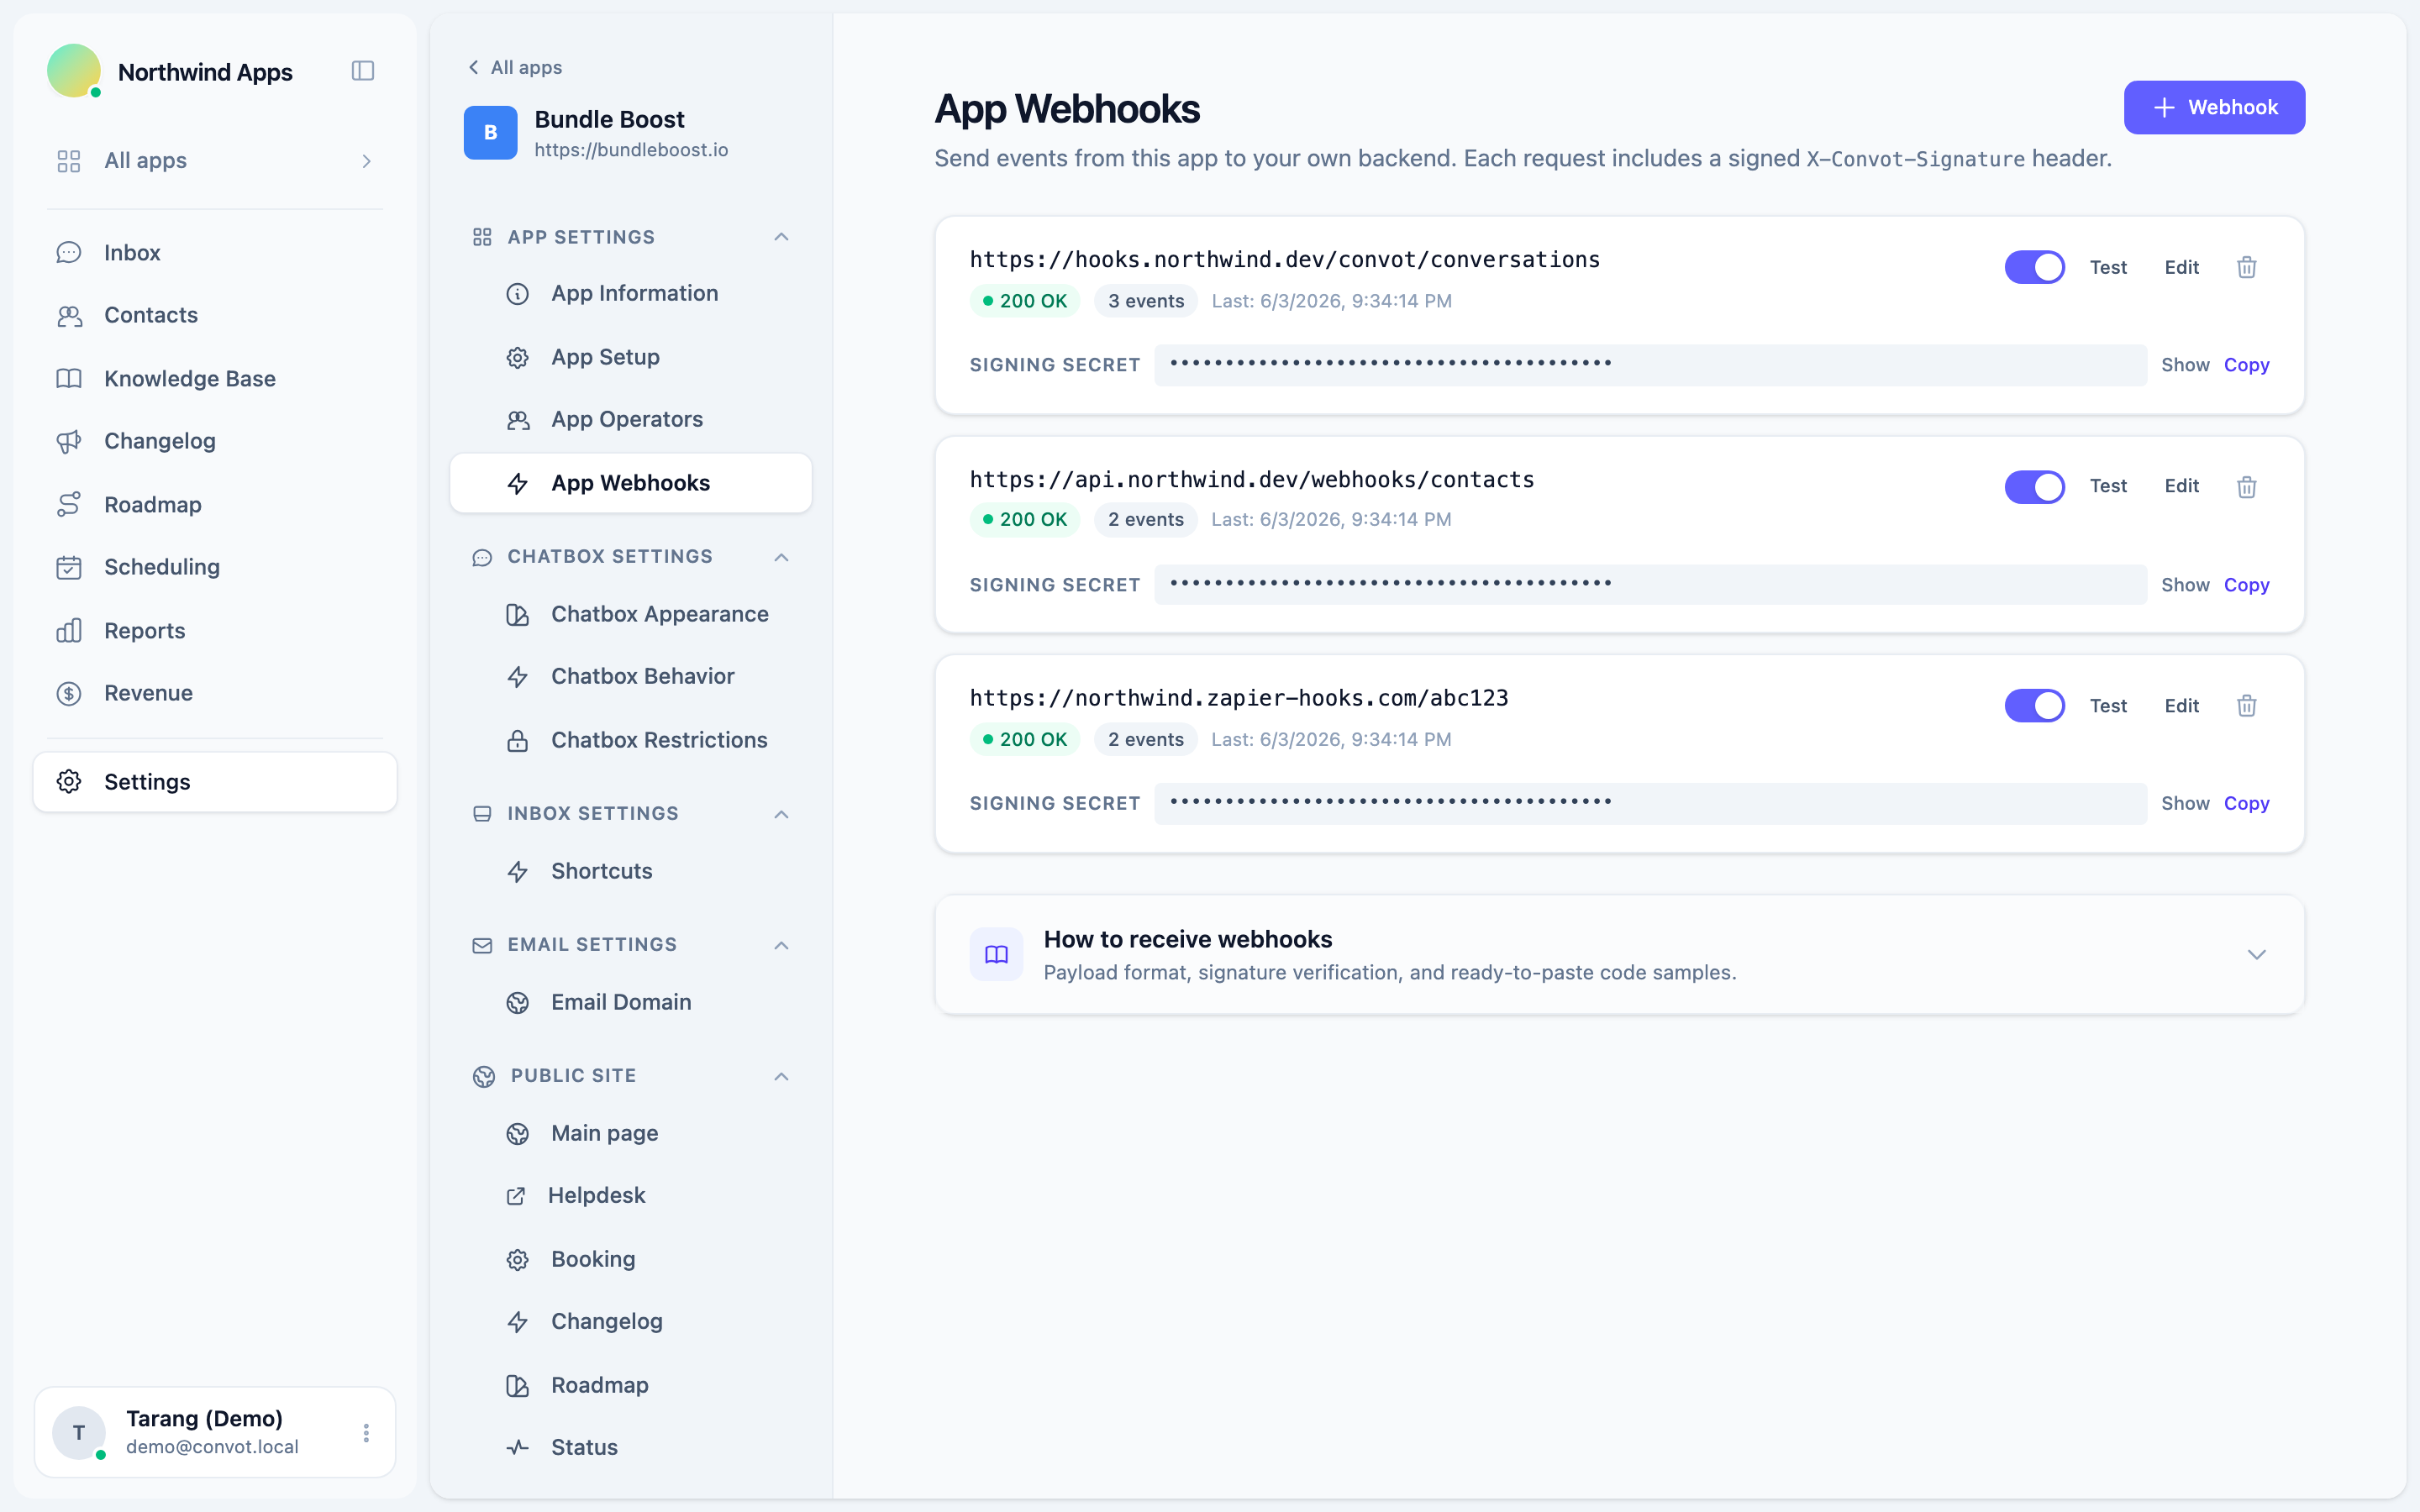
talking to. Nine signed webhooks, a REST API, and an MCP server for your AI agents.
<script>
  window.Convot =  app_id: "your_app_key" ;
</script>
<script async src="https://app.convot.io/widget-loader.js"></script>


<script>
  Convot.push(["set", "user:email", "[email protected]"]);
  Convot.push(["set", "user:nickname", "Maya Chen"]);
  Convot.push(["set", "session:data",
    company: "Acme",
    plan: "Pro",
  ]);
</script>Every integration primitive you need, nothing you don't.
One embed per app, every conversation in one inbox, identity built in. Works in any web app, site or Shopify app.
One-line embed
Drop two script tags into each app's <head> and
you're live. Sandboxed iframe, smart sizing, zero dependencies, it cannot
break your page.
$crisp-compatible SDK
Convot.push(["set", ...]) mirrors the Crisp SDK exactly,
user email/nickname/avatar/company, session data, segments, and events.
Trigger the widget too: open chat, deep-link a help article, or pop the
booking flow with Convot.openScheduling(). Migrate without
rewriting a line of host-page code.
HMAC identity verification
Sign the visitor's identity server-side with your app's secret key.
Enable require_identity_verification and Convot rejects
any unverified session, no spoofing, no shared-device leakage.
9 signed webhooks
Every event you need: message sent/received/deleted, conversation
created/assigned/resolved/reopened, contact created/identified.
Each delivery signed with a per-webhook whsec_ HMAC you verify
server-side.
REST API
Full programmatic access over a scoped /v1 API: send messages,
manage conversations and contacts, and publish help-center, changelog, and
roadmap content. Authenticated with revocable per-app keys and granular scopes.
Read the API reference →
Session data, segments & events
Push custom key/values (session:data), tag contacts with
segments, and fire timeline events, all visible in the agent sidebar so
your team sees context before they reply.
Cryptographically prove who you're talking to.
Compute the HMAC server-side so the secret never leaves your backend. Enable enforcement in one toggle and Convot rejects unsigned sessions.
# Generate the user_hash on your backend before rendering the page
require "openssl"

identity_secret = ENV["CONVOT_IDENTITY_SECRET"]   # from app settings
user_id         = current_user.id.to_s   # or their email

user_hash = OpenSSL::HMAC.hexdigest(
  "SHA256",
  identity_secret,
  user_id
)

# Pass user_hash to the frontend and identify the user
# Convot.identify({ external_id: user_id, email: user.email, user_hash: user_hash });
// Generate the user_hash on your backend before rendering the page
import createHmac from "crypto";
const identitySecret = process.env.CONVOT_IDENTITY_SECRET; // from app settings
const userId = String(user.id); // or their email
const userHash = createHmac("sha256", identitySecret)
.update(userId)
.digest("hex");
// Pass userHash to the frontend and identify the user
// Convot.identify({ external_id: userId, email: user.email, user_hash: userHash });Pass a signed shop domain, and revenue shows up beside the chat.
Building a Shopify app? Pass the merchant's shop domain with a signed
shop_hash in Convot.identify, and Convot links the contact to
your Shopify Partner sync. Plan, MRR and LTV appear in the agent sidebar automatically.
No extra API calls from your app required.
Also worth knowing
Integrations
Slack with per-app channels, Google Meet, Postmark, Cloudflare custom domains, webhooks, and the Shopify Partner API.
See integrations →Live chat & widget
The widget you embed, appearance, behavior, section toggles, and away states.
See live chat →Revenue intelligence
For Shopify apps: what merchants look like to agents when the widget identifies them.
Explore revenue →Embed Convot in every app today.
Start free, no credit card. Two lines of code, live in minutes.